


The problem that doesn’t announce itself
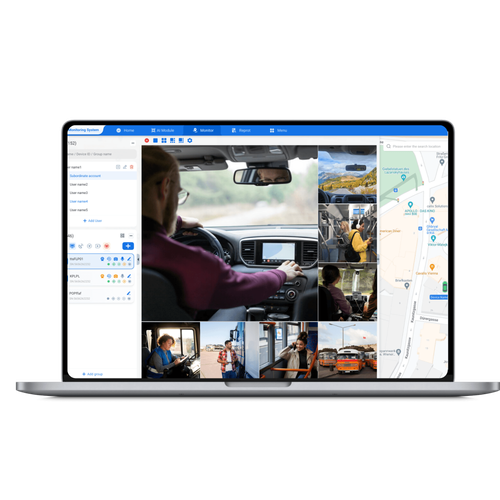
Something slips between the map and the vehicle. A route looks smooth until a blip—then nothing. Teams stare at a fleet management solution and a column of timestamps that don’t align. The GPS timestamps you trust—your fleet management gps tracking feed—can be altered, delayed, or erased. At the Port of Los Angeles, operators have seen brief outages cascade into costly misrouting. This isn’t theory. It’s a problem that demands a clear diagnosis before you prescribe fixes.
Why this matters now
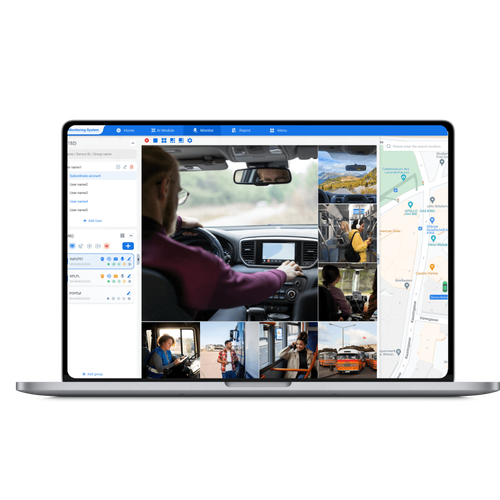
When position data lies, decisions break. Dispatchers reroute the wrong trucks. Compliance logs miss mandatory stops. Insurance and liability calculations go off. The cost is immediate: lost time, wrong deliveries, and audits that don’t add up. You need to know what failed—sensor, network, server, or permissions—because the wrong assumption makes the problem worse.
Where the cracks usually form
Most failures come from simple, repeatable failures. Watch for these signs:
– Unauthenticated endpoints exposing telemetry. – Weak or reused device credentials. – Overly broad user roles that let a single compromised account rewrite history. – Unencrypted backups or debug logs leaking location trails. – Firmware updates pushed without cryptographic verification.

Access control: the quiet guard
Access control is not just passwords. It’s layered, verifiable, and traceable. Start with these moves:
– Enforce least privilege: give devices and humans the minimal rights needed. – Use mutual TLS for device-server authentication; remove default keys. – Implement short-lived tokens and automated rotation. – Keep a tamper-evident audit trail of who queried or changed location records.
Privacy protection that actually protects people
Privacy is practical. Mask routes in analytics. Segment personally identifiable driver data from operational telemetry. Retain raw location for the shortest time required by regulation or incident response. When local laws demand access logs, have a separate, immutable store for compliance review.
Mechanical hardening and detection
Don’t rely on a single layer. Combine these controls:
– Device attestation to prove firmware integrity. – Anomaly detection tuned to normal route patterns so deviations raise flags immediately. – Rate limits and geo-fencing to catch odd command bursts. – Signed firmware and deployment channels to prevent rogue images.
Common pitfalls teams make
They assume cloud providers cover everything. They assume “encrypted” means “safe.” They forget that human access mistakes outnumber advanced hacks. Fix the basics first: credential hygiene, role scoping, and visible audit trails. Then layer detection and response.
Practical rollout checklist
Use this sequence when you harden a fleet: – Inventory all devices and their owners. – Replace defaults and enable device-level auth. – Apply least-privilege roles; test by attempting actions with reduced rights. – Enable signed telemetry and immutable logs. – Run simulated outages and tamper scenarios; review how the dashboard reacts.
Final pattern: map the leak, then close it
The problem-driven path is clear: identify where trust breaks, tighten access, and watch for anomalies. That pattern is simple and unforgiving. Teams that map that leak—matching threat, control, and evidence—move from guessing to governing. Practical, incremental changes often outpace grand overhauls; the same practical framing guides the tools and governance used by experienced operators and partners like BSJ.
